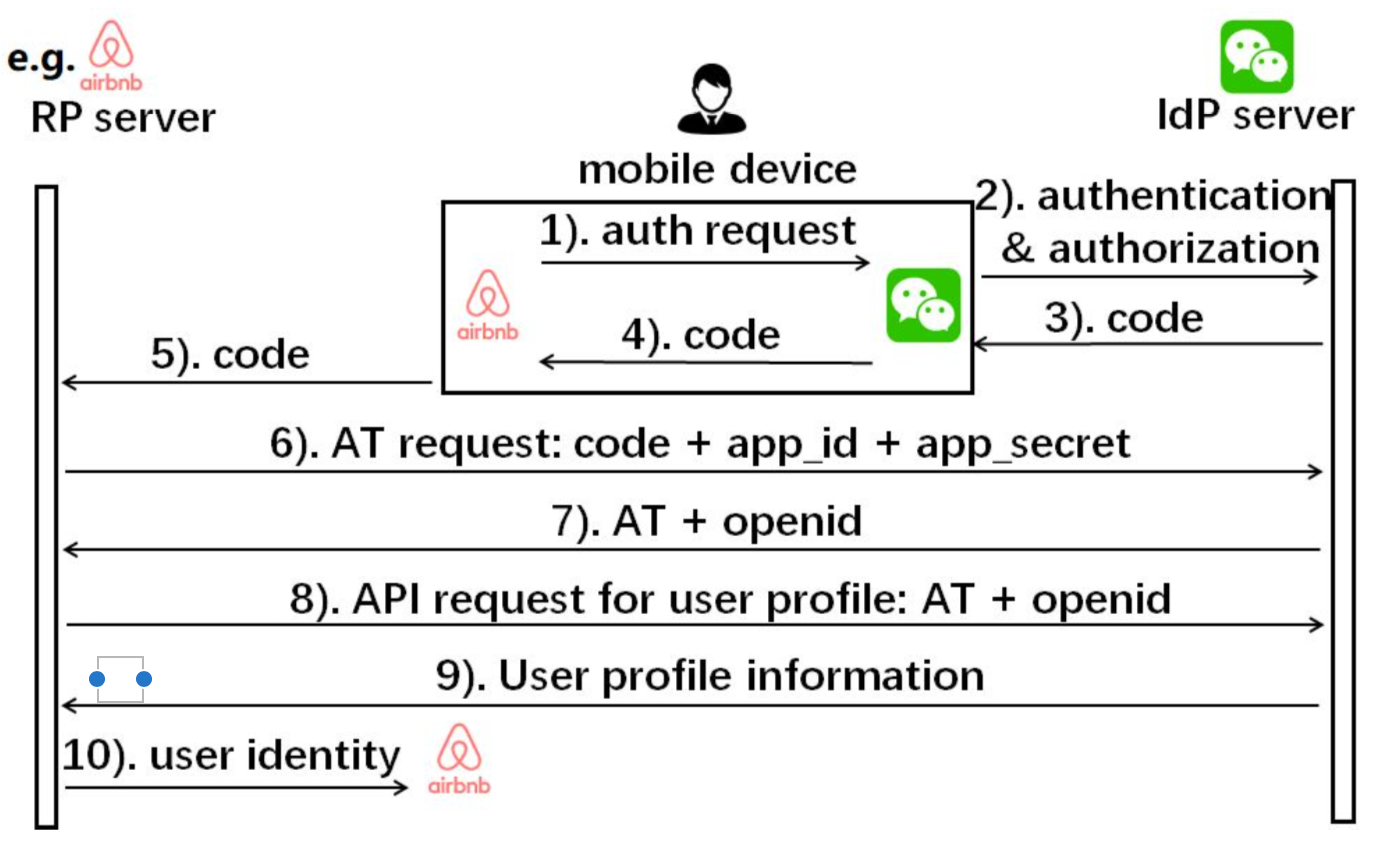
According to the RFC6749 [1], the code used in the authorization code grant flow (in Fig. 1) should be short-lived and the WeChat developer document also claims that the valid time of the code is 10 minutes. We found that an unused code generated more than 100 minutes ago can still be used to exchange for a valid access token. Thus, the WeChat server, in fact, does not maintain the code properly.
Though the vulnerability cannot be exploited directly, it increases the chance for an attacker to consume the stolen code so as to hijack the RP account of the victim. All the RP apps that integrate the SSO service from WeChat are affected by the issue.
It is the IdP server’s duty to fix the vulnerability, where the server should verify the issued time of every incoming code and reject the expired ones.
[1] RFC6749