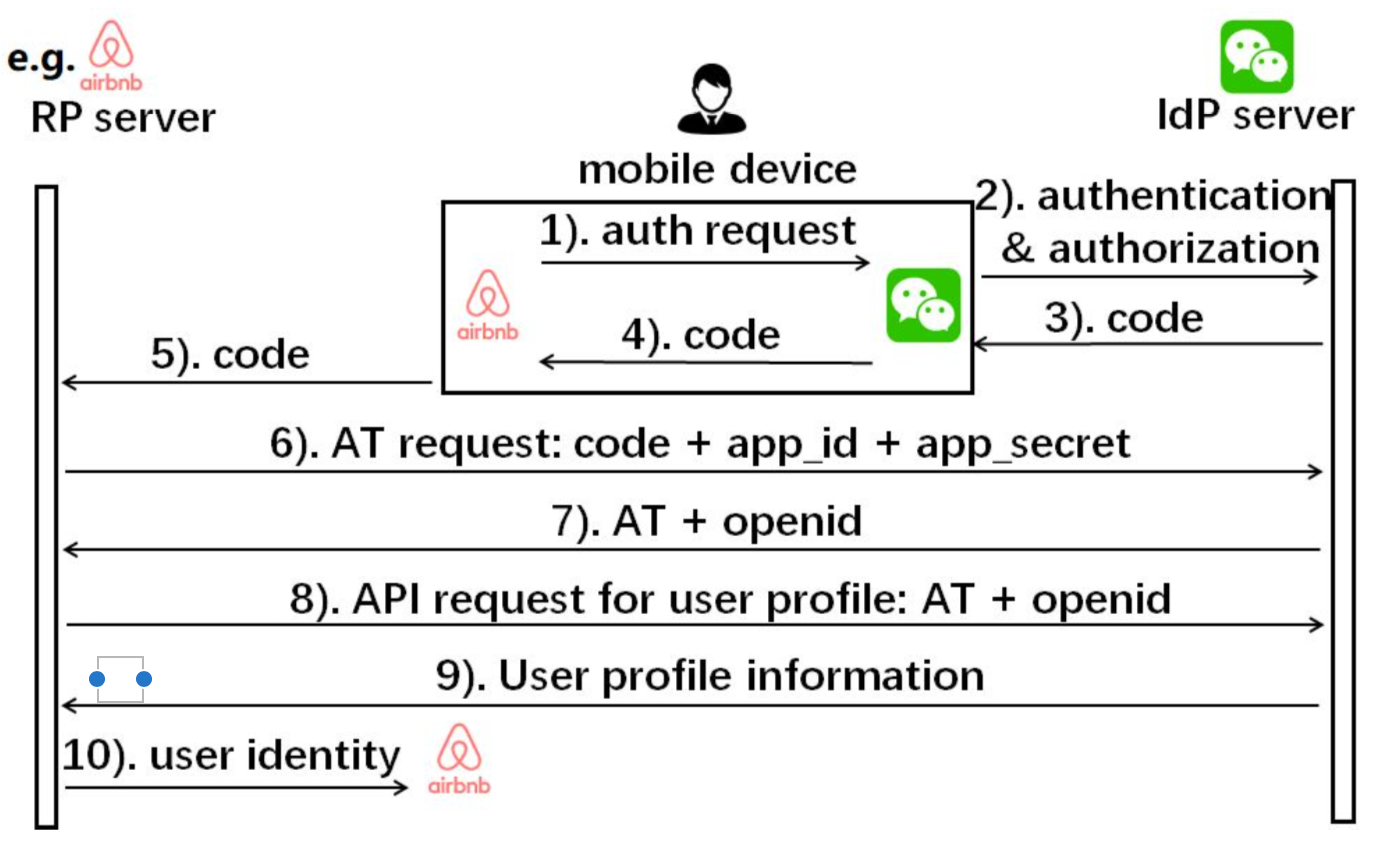
RP developers may deploy the server-to-server logics on its client side (RP app). Some of the interactions include the app secret, so the RP developers tend to include the secret in their APK, which may be stolen by the attacker via. reverse engineering or analyzing real-time SSO network traffic. Worse still, even if the RP developers fix the issue in their latest app, the attacker can still decompile the APKs of history versions to get the secret.
The app secret is the identity proof issued by the IdP to RP. With the app secret, the attacker can impersonate as the benign RP. Thus, he is able to exchange the stolen code for a valid access token (Step 6 in Fig. 1) and further extract victim’s user profile on the IdP server with the token. In addition, since Facebook utilizes the same secret to sign the user profile (right before Step 3 in Fig. 1), the attacker is capable of forging a valid signature to launch the profile attack.
The RP developers should check all the history versions of their app. Once the app secret is leaked, RP should renew its value on the IdP.